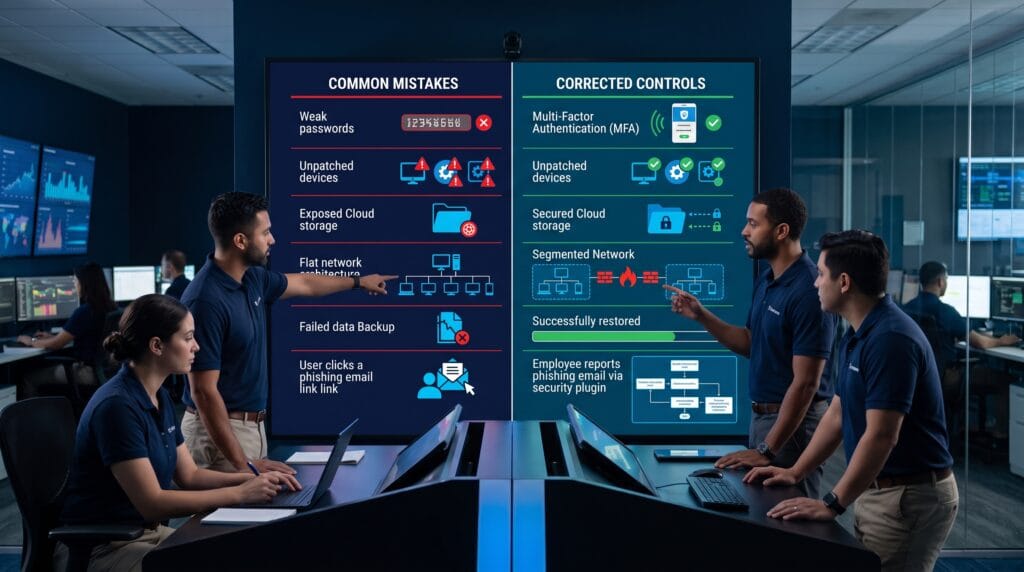
Cybersecurity incidents rarely begin with one dramatic technical failure. They often begin with ordinary decisions that appear harmless: an unused account remains active, a critical update is delayed, an employee receives more access than necessary, a cloud folder is shared publicly, or a backup is created but never tested. Understanding common cybersecurity mistakes helps organizations correct these weaknesses before attackers combine them into a serious incident.
The most damaging mistake is treating security as a one-time technology purchase. Firewalls, endpoint tools, email filters, and cloud controls are useful, but they only work when responsibilities are clear, configurations are maintained, alerts are investigated, and recovery plans are exercised.
The NIST Cybersecurity Framework 2.0 organizes cybersecurity outcomes around six functions, Govern, Identify, Protect, Detect, Respond, and Recover. This structure shows that cybersecurity includes leadership, asset visibility, preventive controls, monitoring, incident management, and operational recovery.
This guide explains 18 common cybersecurity mistakes, why they create risk, and how organizations can avoid them through practical controls, ownership, measurement, and continuous improvement.
Why Common Cybersecurity Mistakes Persist
Many security weaknesses are not caused by a lack of tools. They persist because organizations face:
- Limited budgets
- Competing operational priorities
- Unclear ownership
- Rapid technology changes
- Complex vendor relationships
- Skills shortages
- Legacy systems
- Incomplete inventories
- Weak communication between teams
- A belief that an incident will not happen
Attackers benefit from inconsistency. One forgotten server, one privileged account without multifactor authentication, or one exposed remote-access service may be enough.
Organizations should therefore focus on repeatable security processes rather than occasional emergency projects.
1. Treating Cybersecurity as Only an IT Responsibility
Cybersecurity affects legal obligations, finance, operations, customer trust, employee safety, communications, and business continuity.
Why This Is a Mistake
When security is delegated entirely to IT:
- Business leaders may not understand the risk.
- Security spending competes poorly with visible projects.
- Legal and communication decisions are delayed.
- Business owners may ignore risky processes.
- Responsibility becomes unclear during an incident.
How to Avoid It
Establish executive accountability and a cross-functional security group.
Include representatives from:
- Technology
- Operations
- Legal
- Finance
- Human resources
- Communications
- Procurement
- Business leadership
Review cyber risk alongside other enterprise risks.
Practical Control
Assign an owner to every major security capability, including identity, patching, backups, incident response, vendor risk, and employee awareness.
2. Failing to Maintain an Accurate Asset Inventory
Organizations cannot secure devices, software, cloud resources, and accounts they do not know exist.
Common Inventory Gaps
- Old servers
- Forgotten websites
- Unapproved SaaS tools
- Personal devices
- Test cloud environments
- Service accounts
- Internet of Things devices
- Unsupported software
- Former employee accounts
- Supplier connections
Why This Is a Mistake
Unknown assets may remain:
- Unpatched
- Misconfigured
- Unmonitored
- Publicly exposed
- Connected to sensitive systems
How to Avoid It
Create a continuously updated inventory covering:
- Hardware
- Software
- Cloud services
- SaaS applications
- Domains
- Data repositories
- Users
- Service accounts
- Third-party connections
Record ownership, criticality, exposure, support status, and data sensitivity.
3. Relying on Passwords Alone
Passwords are frequently stolen through phishing, credential reuse, malware, social engineering, and data breaches.
Why This Is a Mistake
A valid password can allow an attacker to appear like a legitimate user.
Password complexity alone does not stop:
- Credential phishing
- Session theft
- Password spraying
- Reused credentials
- Help-desk manipulation
How to Avoid It
Enforce multifactor authentication for:
- Remote access
- Cloud administration
- Financial systems
- Customer databases
- Privileged accounts
- Important SaaS platforms
Prefer phishing-resistant methods such as passkeys or hardware security keys where practical. CISA recommends phishing-resistant MFA as a foundational protection, particularly for critical services and high-value accounts.
Additional Controls
- Use a password manager.
- Block known compromised passwords.
- Disable legacy authentication.
- Monitor unusual sign-ins.
- Protect account-recovery processes.
4. Giving Users Too Much Access
Excessive access increases the damage from compromised or misused accounts.
Common Examples
- Employees retain permissions after changing roles.
- Contractors keep access after projects end.
- Standard users have local administrator rights.
- Shared administrator accounts are used.
- Service accounts receive broad permissions.
- Former employees remain active.
How to Avoid It
Apply the principle of least privilege.
Use:
- Role-based access
- Separate administrator accounts
- Time-limited privileged access
- Automated onboarding and offboarding
- Quarterly access reviews
- Approval workflows
- Service-account ownership
- Credential rotation
Important Practice
Do not use privileged accounts for email, browsing, or routine work.
5. Delaying Security Updates and Patches
Known vulnerabilities are attractive because attackers can automate scanning and exploitation.
Why Organizations Delay
- Fear of downtime
- Incomplete testing
- Legacy dependencies
- Unclear ownership
- Poor inventory
- Limited maintenance windows
How to Avoid It
Build a formal vulnerability and patch-management process.
Prioritize based on:
- Active exploitation
- Internet exposure
- Business criticality
- Data sensitivity
- Available privileges
- Severity
- Compensating controls
CISA’s vulnerability-response guidance emphasizes accelerated action for vulnerabilities actively exploited in the wild.
Practical Controls
- Scan regularly.
- Patch operating systems, applications, firmware, and network equipment.
- Remove unsupported systems.
- Track exceptions.
- Verify remediation.
- Report overdue critical vulnerabilities to leadership.
6. Using Default or Insecure Configurations
Default settings often prioritize ease of deployment rather than security.
Common Configuration Mistakes
- Default passwords
- Unnecessary open ports
- Public cloud storage
- Disabled logging
- Weak encryption
- Unrestricted remote administration
- Insecure file sharing
- Excessive cloud permissions
- Unused services
- Open database access
How to Avoid It
Create approved secure configuration baselines for:
- Workstations
- Servers
- Cloud environments
- Network devices
- Databases
- Containers
- Mobile devices
Use automated configuration monitoring to detect drift.
7. Operating a Flat Network
A flat network allows users and systems to communicate broadly.
Why This Is a Mistake
After compromising one device, an attacker may move toward:
- Servers
- Backups
- Payment systems
- Administrative tools
- Sensitive databases
- Operational technology
How to Avoid It
Segment the network based on function and risk.
Separate:
- Employee devices
- Servers
- Backups
- Guest networks
- IoT devices
- Payment systems
- Development environments
- Administrative interfaces
Apply firewall rules and monitor traffic between segments.
8. Neglecting Email and Phishing Protection
Phishing remains a common route for credential theft, malware, invoice fraud, and account compromise.
Common Mistakes
- Relying only on spam filtering
- Allowing risky attachment types
- Ignoring domain impersonation
- Failing to authenticate email
- Not verifying payment changes
- Punishing employees who report mistakes
How to Avoid It
Use:
- Advanced email filtering
- Attachment analysis
- Link protection
- Impersonation detection
- External sender labels
- User reporting tools
- Account-takeover monitoring
- Payment-verification procedures
Configure SPF, DKIM, and DMARC for organizational domains.
Also Read: What Is Cybersecurity? Complete Beginner’s Guide
9. Depending on Security Awareness Training Alone
Training is important, but employees cannot compensate for weak technical controls.
Why This Is a Mistake
Even careful users can be deceived by:
- Realistic phishing
- Compromised supplier accounts
- Deepfake voice calls
- Stolen browser sessions
- Malicious advertisements
- Misleading login pages
How to Avoid It
Combine training with:
- MFA
- Email filtering
- Browser protection
- Payment verification
- Least privilege
- Endpoint detection
- Easy incident reporting
Improve Training
Make it:
- Role-specific
- Short and frequent
- Relevant to current threats
- Supported by realistic exercises
- Focused on reporting
Finance, executives, administrators, developers, and support teams need additional training for their specific risks.
10. Assuming Antivirus Is Complete Endpoint Security
Traditional antivirus is useful but insufficient against attacks that use legitimate tools, scripts, stolen credentials, or fileless techniques.
How to Avoid It
Use centrally managed endpoint detection and response.
Capabilities should include:
- Behavioral detection
- Device isolation
- Investigation timelines
- Script monitoring
- Host firewall
- Disk encryption
- Application control
- Automated containment
- Central policy management
Also manage phones and tablets with mobile-device controls.
11. Creating Backups Without Testing Recovery
A backup is only valuable when it can be restored securely and within the required time.
Common Backup Mistakes
- Backups remain connected to the same network.
- Backup administrators use ordinary accounts.
- Copies are not encrypted.
- Cloud SaaS data is assumed to be fully recoverable.
- Restoration is never tested.
- Recovery priorities are undefined.
- Attackers can delete backup copies.
How to Avoid It
Maintain multiple copies using different storage methods, with at least one protected, isolated, or offline copy.
Test:
- Individual file restoration
- Database recovery
- Server recovery
- SaaS data recovery
- Full business-service restoration
CISA recommends offline, encrypted backups and practiced recovery processes as central ransomware defenses.
12. Failing to Monitor Security Logs
Organizations may own security tools but fail to review the data they generate.
Why This Is a Mistake
Without monitoring, suspicious activity may continue unnoticed.
Important warning signs include:
- New administrator accounts
- Unusual sign-in locations
- Disabled security tools
- Large data downloads
- New email-forwarding rules
- Backup deletion
- Unexpected remote-access software
- Unusual cloud API activity
How to Avoid It
Centralize important logs in a SIEM or managed detection platform.
Collect logs from:
- Identity systems
- Endpoints
- Firewalls
- DNS
- Cloud platforms
- Servers
- Databases
- Backup systems
- Privileged-access tools
Define who investigates alerts and how quickly.
13. Generating Too Many Low-Value Alerts
More alerts do not automatically create better security.
Why This Is a Mistake
Alert overload causes:
- Analyst fatigue
- Delayed investigations
- Inconsistent responses
- Missed critical events
- Poor trust in security tools
How to Avoid It
Tune detections around meaningful attacker behavior.
For every alert, define:
- Why it matters
- Required data
- Investigation steps
- Escalation criteria
- Response authority
- Expected completion time
Remove alerts that repeatedly produce no useful action.
14. Trusting Cloud Providers to Handle Everything
Cloud security uses a shared-responsibility model. Providers secure parts of the infrastructure, while customers remain responsible for identities, permissions, configurations, data, and workloads.
Common Cloud Mistakes
- Public storage
- Excessive administrator access
- Exposed keys
- Missing logs
- Unmanaged test accounts
- Unrestricted integrations
- Weak tenant settings
- No SaaS inventory
How to Avoid It
Use:
- Centralized identity
- Strong administrator authentication
- Cloud-security posture management
- Permission reviews
- Encryption
- Key management
- Public-exposure detection
- Logging
- Backup and recovery
Review SaaS sharing settings, integrations, retention, and offboarding.
15. Ignoring Third-Party and Supply-Chain Risk
Suppliers may access organizational data, systems, networks, facilities, or development environments.
Why This Is a Mistake
A trusted vendor can become an indirect attack path.
How to Avoid It
Create a risk-based vendor program:
- Classify suppliers by access and criticality.
- Review security before purchase.
- Include contractual requirements.
- Limit access.
- Monitor critical providers.
- Include vendors in incident planning.
- Revoke access at termination.
NIST’s supply-chain quick-start guidance recommends including relevant suppliers in cybersecurity incident planning, response, and recovery.
Important Questions
- What data can the vendor access?
- Where is it stored?
- Are subcontractors involved?
- How are incidents reported?
- How quickly can access be removed?
- Can data be returned or deleted?
16. Collecting and Keeping Too Much Data
Organizations often retain information because storage is inexpensive or because deletion has not been assigned to anyone.
Why This Is a Mistake
Unnecessary data increases:
- Breach impact
- Legal exposure
- Investigation complexity
- Backup volume
- Recovery time
- Storage cost
How to Avoid It
Implement:
- Data classification
- Retention schedules
- Secure deletion
- Access controls
- Encryption
- Data-loss prevention
- Collection minimization
Keep data only when there is a clear business, legal, or operational need.
17. Having an Incident Response Plan That Is Never Tested
A written plan may fail when contacts are outdated, authority is unclear, backups are unavailable, or external support cannot be reached.
How to Avoid It
Create scenario playbooks for:
- Ransomware
- Business email compromise
- Data exposure
- Cloud-account compromise
- Lost devices
- Supplier breaches
- Denial of service
- Insider threats
Run tabletop exercises involving technology, leadership, legal, communications, operations, finance, and external partners.
NIST finalized SP 800-61 Revision 3 in April 2025, emphasizing that incident response should be integrated throughout cybersecurity risk management rather than treated as an isolated activity.
18. Failing to Learn After an Incident
Organizations sometimes restore operations but do not address the conditions that allowed the incident.
Why This Is a Mistake
The same weakness may remain available for another attacker.
How to Avoid It
Conduct a structured review covering:
- Initial access
- Detection failures
- Control failures
- Decision delays
- Communication gaps
- Recovery challenges
- Vendor dependencies
- Documentation problems
Assign corrective actions, owners, deadlines, and verification.
Do not use post-incident reviews to assign blame. Use them to improve the system.
Also Read: Shocking Facts about the Role of Blockchain in Cybersecurity
Common Cybersecurity Mistakes Comparison Table
| Mistake | Likely Consequence | Priority Fix |
|---|---|---|
| No executive ownership | Inconsistent security decisions | Assign accountability |
| Incomplete asset inventory | Unknown exposure | Discover and classify assets |
| Password-only access | Account takeover | Enforce strong MFA |
| Excessive privileges | Greater breach impact | Apply least privilege |
| Delayed patches | Exploitation of known flaws | Risk-based patching |
| Weak configurations | Public exposure | Secure baselines |
| Flat network | Easier lateral movement | Segment critical systems |
| Weak email controls | Phishing and fraud | Layered email security |
| Training-only strategy | Preventable account compromise | Add technical controls |
| Untested backups | Failed recovery | Restore testing |
| Missing log monitoring | Late detection | Centralize and investigate |
| Alert overload | Missed critical activity | Tune high-value detections |
| Cloud assumptions | Misconfiguration and leakage | Review shared responsibilities |
| Ignored vendors | Supply-chain compromise | Risk-based vendor management |
| Excess data retention | Larger breach impact | Minimize and delete |
| Untested response plan | Confused crisis response | Exercise playbooks |
| No lessons learned | Repeated incidents | Track corrective actions |
How to Prioritize Cybersecurity Improvements
1. Identify Critical Services
Document the systems required to:
- Deliver products
- Serve customers
- Collect revenue
- Pay employees
- Communicate
- Meet legal obligations
2. Find the Most Dangerous Gaps
Look for:
- Administrators without MFA
- Internet-facing unpatched systems
- Unsupported software
- Unmanaged devices
- Public data exposure
- Backups that have not been tested
- Missing incident contacts
- Critical vendor access
3. Fix Foundational Controls
Prioritize:
- Asset inventory
- MFA
- Privileged access
- Patching
- Endpoint management
- Email protection
- Protected backups
- Logging
- Incident response
4. Measure Coverage
Track:
- Percentage of accounts using MFA
- Percentage of managed endpoints
- Patch compliance
- Age of critical vulnerabilities
- Number of privileged accounts
- Backup-restoration success
- Alert-investigation time
- Incident-response exercise completion
- Vendor-assessment coverage
5. Review Regularly
Technology, staff, suppliers, and risks change continuously.
Common Cybersecurity Mistakes Checklist
Use this common cybersecurity mistakes checklist during a security review:
- Cybersecurity has executive ownership.
- All important assets and accounts are inventoried.
- Critical accounts use phishing-resistant MFA where practical.
- Privileged access is separate and limited.
- Former users are removed promptly.
- Critical vulnerabilities are prioritized.
- Unsupported software is being replaced.
- Secure configuration baselines exist.
- Important network areas are segmented.
- Email authentication and phishing controls are configured.
- Endpoints are centrally managed.
- Backups are protected from ordinary administrator accounts.
- Recovery tests are completed.
- Important logs are centralized.
- Alerts have owners and response procedures.
- Cloud and SaaS settings are reviewed.
- Sensitive data has retention rules.
- Critical vendors are assessed.
- Incident playbooks are exercised.
- Post-incident actions are tracked to completion.
Frequently Asked Questions
1. What Is the Most Common Cybersecurity Mistake?
There is no single mistake in every organization, but weak identity protection, delayed patching, incomplete asset inventories, and untested backups are recurring weaknesses.
2. Is Employee Training Enough to Prevent Cyberattacks?
No. Training should be combined with MFA, email filtering, endpoint protection, access controls, monitoring, and easy reporting.
3. Why Is Multifactor Authentication So Important?
MFA adds another barrier when a password is stolen. Phishing-resistant MFA provides stronger protection for administrators, email, remote access, and critical systems.
4. How Often Should Backups Be Tested?
Testing frequency should match the importance and rate of change of the system. Critical services should be tested regularly and after major infrastructure changes.
5. How Often Should an Incident Response Plan Be Exercised?
Organizations should exercise plans regularly and after major changes in systems, staff, suppliers, or legal obligations. Higher-risk organizations may test several scenarios each year.
6. Can Small Businesses Avoid These Mistakes Without a Large Security Team?
Yes. Small organizations can prioritize managed devices, MFA, automatic patching, email protection, protected backups, a managed detection service, and a simple incident-response plan.
Conclusion on Common Cybersecurity Mistakes
Most common cybersecurity mistakes are preventable when organizations establish clear ownership and maintain basic controls consistently.
The greatest risks often come from ordinary gaps: unknown assets, stolen credentials, excessive access, delayed patches, weak configurations, flat networks, untested backups, missing monitoring, unmanaged vendors, and incident plans that exist only on paper.
Start with the systems and accounts that matter most. Enforce strong authentication, reduce privileges, patch exposed systems, protect backups, centralize security visibility, and test response procedures before an emergency.
Cybersecurity maturity does not come from avoiding every mistake forever. It comes from finding weaknesses early, correcting them systematically, and learning faster than the threat environment changes.
Also Read: “30 Cybersecurity Best Practices Every Business Should Follow“